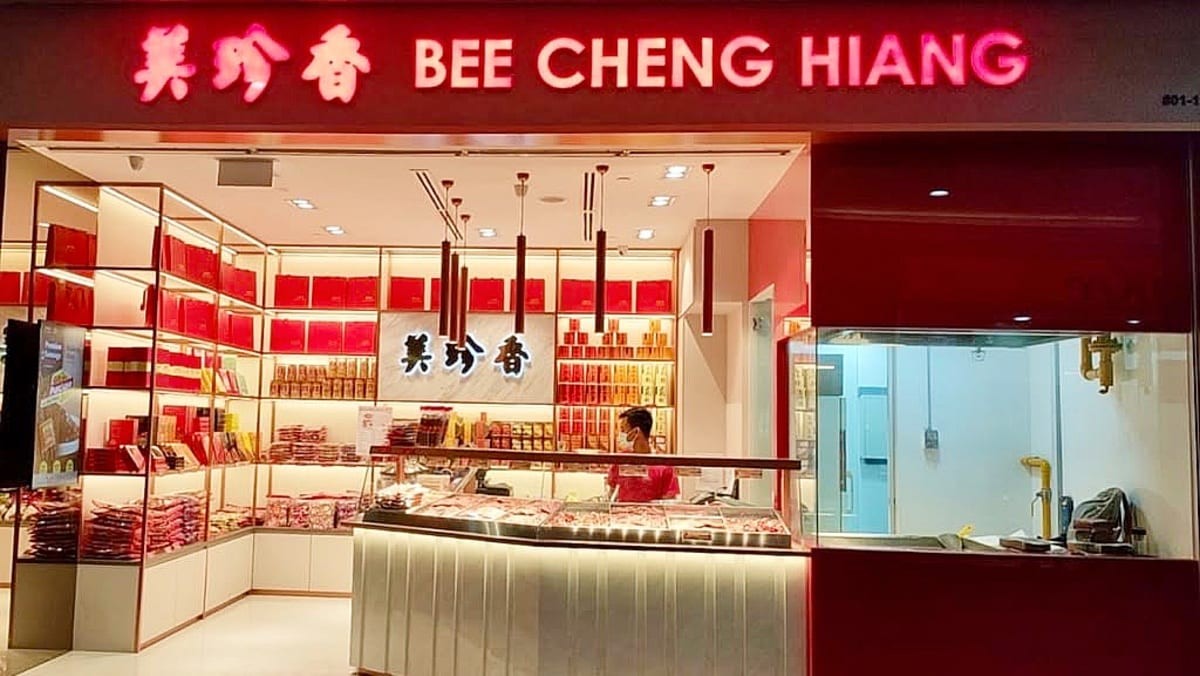
Bee Cheng Hiang, the Singapore company that has sold bak kwa, or barbecued pork jerky, for close to a century, decided in April to try something new. An employee asked an artificial-intelligence tool to write a short program that would send the company’s promotional emails to a large batch of customers at once. It was the first time the company had used an AI tool for its business operations. It did not go well.
The program the employee deployed was meant to send the emails in batches of 1,000. Because of a coding error, it did something else: every recipient in each batch could see the email addresses of the other recipients. The flaw came down to two brackets placed in the wrong position in the Python code, according to the Personal Data Protection Commission, the city-state’s privacy regulator. The emails went out on April 25. Bee Cheng Hiang reported the breach to the commission on April 27.
More than 95,000 customers had their email addresses exposed. It was Singapore’s first reported data breach tied to the use of an AI tool, the commission said, and the exposure was limited to email addresses, with no evidence the addresses were misused afterward.
The regulator’s account, published on its website on September 21, placed the blame on process as much as on a single mistaken prompt. The employee had not told the AI tool to hide each recipient’s address from the others, so the code it generated sent the batch emails with every address visible. The commission said the failure was human error in developing the distribution code, not a malfunction in the AI tool. It noted that the company had relied on one employee without a review process or supervisory checks, and had no governance framework or policies to guide staff on using generative AI at work.
The employee did not catch the mistake before sending. Testing was done by checking activity logs rather than reviewing the content of an actual test email, so the error slipped through. Once the company confirmed what had happened, it stopped the mass emails, fixed the code and notified affected customers, the commission said.
Bee Cheng Hiang, founded in 1933, is one of Singapore’s best-known homegrown brands, a fixture at Chinese New Year when its sweet, smoky pork jerky is given as a gift. The breach touched its marketing list rather than payment details, which softened the damage, but it hit at something the brand sells above all: trust among a mostly local customer base.
The Personal Data Protection Commission has policed the country’s Personal Data Protection Act since it took force in 2014, and it has built a reputation for naming companies and demanding fixes rather than levying heavy fines at first. Companies that breach the act can be fined up to S$1 million, or 10 percent of annual turnover in Singapore, whichever is higher. The commission accepted a voluntary undertaking from the company on September 2 to improve its compliance. Bee Cheng Hiang agreed to put in place a framework governing how employees use AI for coding, including an independent technical review of any AI-generated code that involves personal data. It has also begun requiring at least two staff members to verify bulk email campaigns before they are sent.
The case is small in scale, but the regulator is treating it as a warning shot for a much larger question. Singapore has positioned itself as an AI hub and wants businesses to adopt the technology quickly, and it has published governance frameworks to encourage responsible use. The commission used the ruling to remind organizations to run data-protection assessments before deploying AI tools and to build review mechanisms around them. For every company that experiments with a coding assistant, the message was to check the work before the work goes out.
The incident is a data-protection case first and an AI story second, and the commission took care to draw the line. The regulator said the exposed addresses were not managed, processed or generated by any AI-powered system; the AI only wrote the code that mishandled them. That distinction matters, because it keeps the accountability on the humans who deploy the tools rather than on the tools themselves, even as Singapore encourages companies to adopt them. For a city-state billing itself as a test bed for AI, the first AI-related breach was always going to be read as a signal about who is watching the machines.
What the episode shows is how thin the margin of error can be: two brackets in a line of code, written with the help of an AI tool by a single employee with no one checking the work. The next test is whether other companies in Singapore read the fine print before they, too, ask a model to write their mailing code.